Conversation


|
How is this new popup show? Is it overlaid to the page itself? |

| matrix: | ||
| node-version: [26.x] | ||
| os: [ubuntu-latest, windows-latest] | ||
| node-version: [24.x, 26.x] |

There was a problem hiding this comment.
This test runs on a single version of node as test-detection is a heavy test that downloads a lot of files to test the repo. This test does not need to be run across multiple OSes and node versions. There will need to be a split
There was a problem hiding this comment.
Moved test-detection.js and its cache into a separate ubuntu-latest / Node 24 job. The other checks remain in the OS/Node matrix.
|
The previous version of the prebuilt chrome extensions also bundle the repository, allowing it to be used with a slightly stale version of the repository even if it cannot download a new version. Use case is copying it in to a network without internet access or where access to github is blocked. |

42be9e8 to
c790318
Compare

|
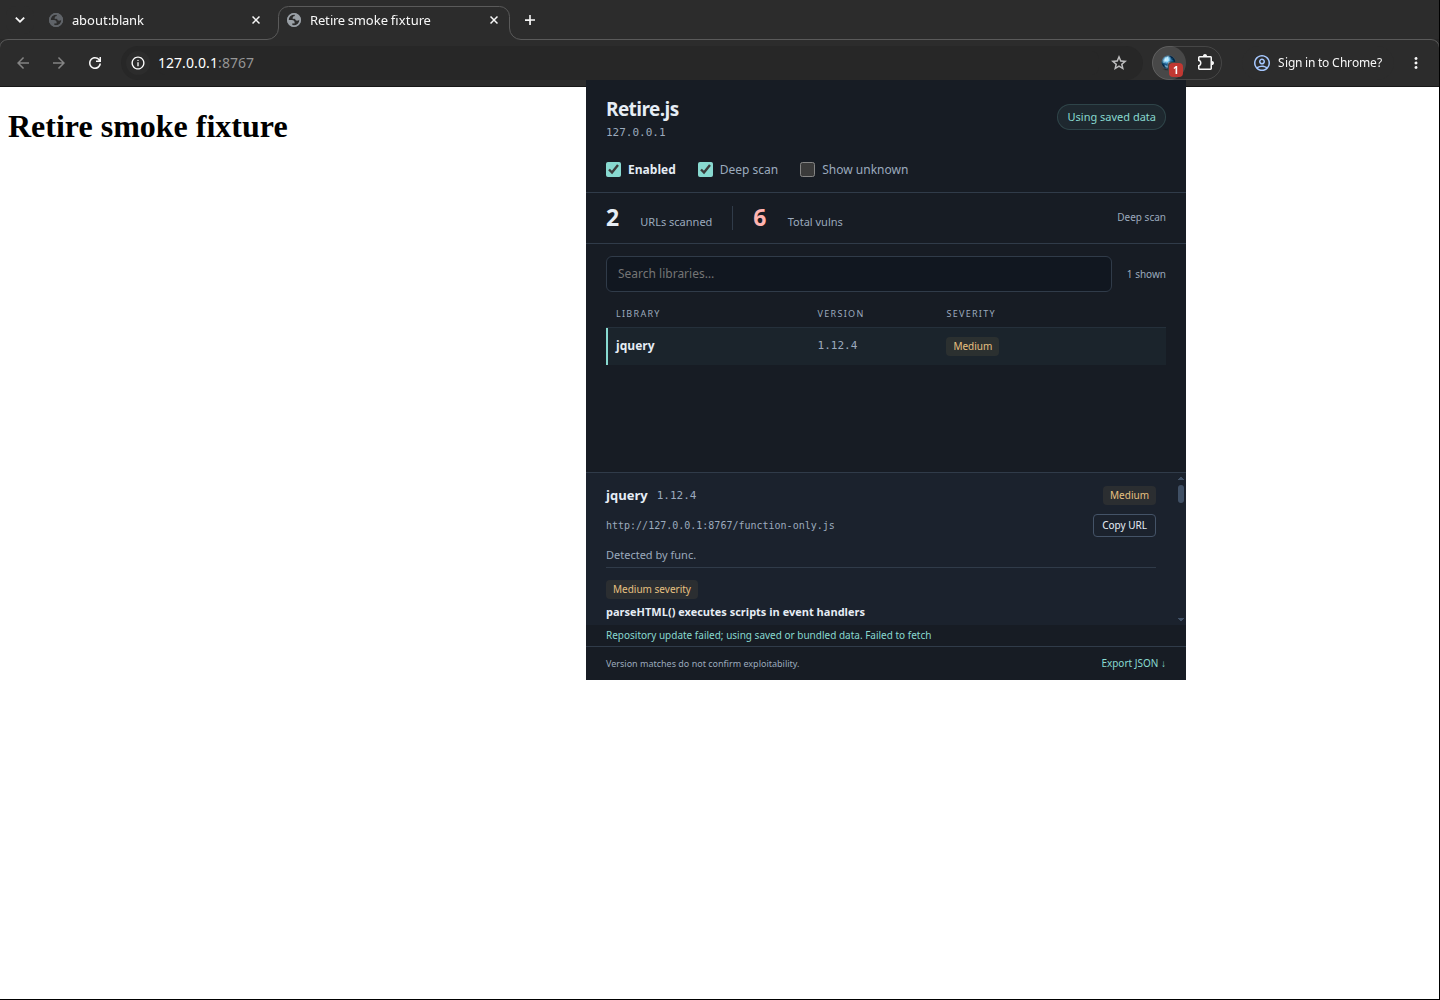
By "popup", I mean the existing extension window that opens when you click retire.js in the browser's top-right toolbar or Extensions menu. This PR redesigns that window; it does not inject anything into the web page. The screenshot below shows the whole Chrome window, including the toolbar button and its native popup, on a local test page. GitHub access was blocked to verify detection using the bundled repository on a fresh profile.
All three prebuilt packages already bundle the advisory repository. I added a regression test for first-launch detection without a cached repository or a successful update, and documented the fallback. Chrome, Chrome no-func, and Firefox browser checks passed. All six PR commits now have verified signatures. Validation: 62 Node tests, 17 extension tests, all 48 detection packages, build, typecheck, and ESLint passed. |
This branch has not been deployed
2 participants


Browser scans could lose or mix results across navigation and background restarts. This PR shares a runtime and popup across Chrome, Chrome without function scanning, and a modern Firefox WebExtension, with session state, stale-result rejection, detector refresh with cached fallback, and regression coverage.
The popup is 600×600 pixels: a searchable resource list above a scrollable library/advisory inspector, with persistent settings, URL copying, and complete JSON export. Failed scans and unidentified resources remain distinct from libraries with no known advisories. Counts and exports remain unfiltered.
Ready to load without Node
Complete prebuilt packages are committed in
dist/chrome,dist/chrome-no-func, anddist/firefox. Download and extract the repository ZIP, then load the appropriate package. Node is needed only for development. Firefox uses temporary add-on installation, which lasts until browser exit.The development instructions recommend Node 24 LTS. Portable build/test scripts support Windows and Linux, and CI covers Node 24 and 26, including a rebuild check for committed packages. The added
--no-audit/--no-fundflags are removed. Generated files are marked as such for review.Actual popup screenshots
Captured with Playwright on September 18, 2026 using Chrome 153 on Google's XSS training page. The loaded jQuery 2.1.1 produces six advisory matches across two script URLs. These are version matches, not exploit confirmations. Firefox shares the UI and was tested separately.
Resource overview and selected library:
The same popup with the inspector scrolled to CVE-2020-11022:
Validation and compatibility
This is the extension-only replacement for #622. CLI and CycloneDX fixes are submitted separately. Native smoke scripts currently use Windows browser installation paths; CI runs the platform-independent tests and builds. No browser-store publishing is included. AI-assisted implementation.
Related independent replacements: CLI fixes #623 and CycloneDX #625.